The lesson
Translate a technical security argument into executive terms, then give leaders the exact questions to take back to their teams.
The move
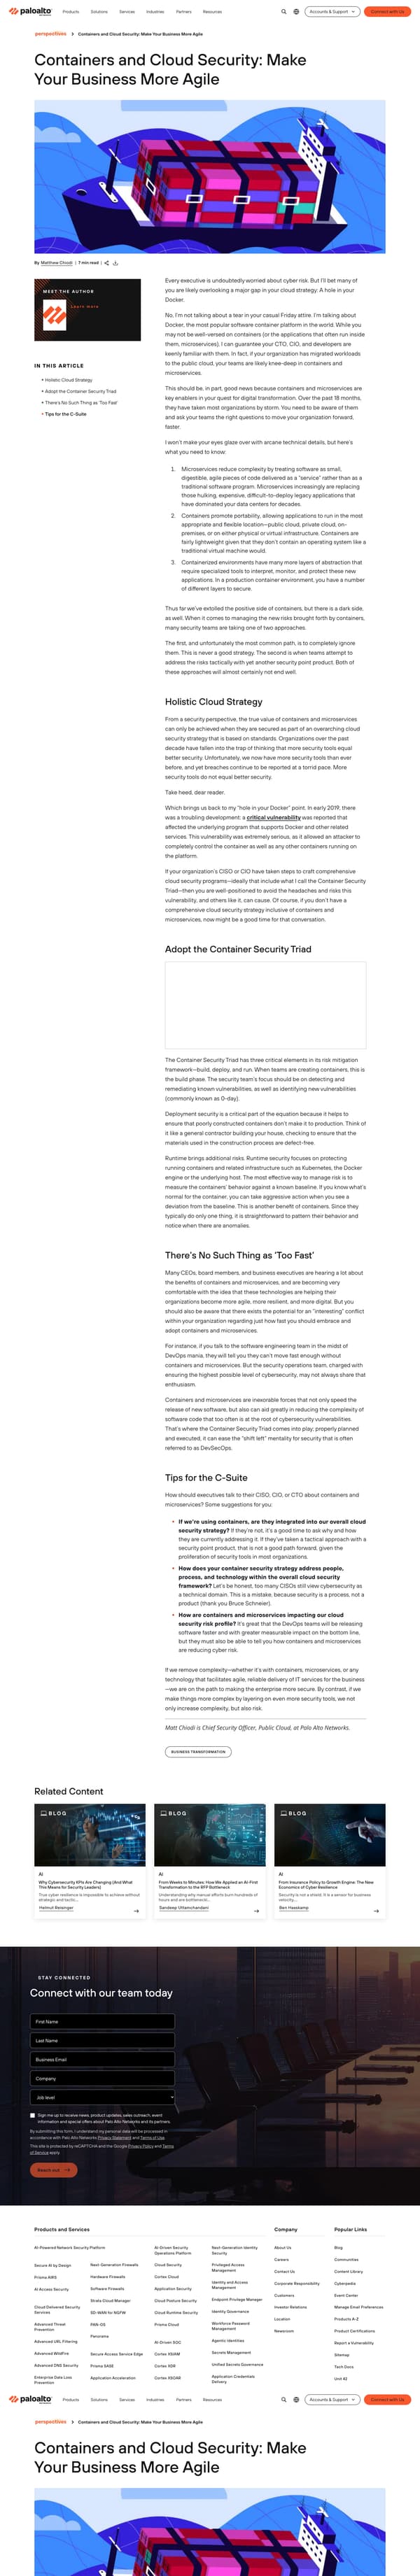
The page opens with the title, byline, read time, and a large illustration of shipping containers, then an “IN THIS ARTICLE” list that previews “Holistic Cloud Strategy,” “Adopt the Container Security Triad,” “There’s No Such Thing as ‘Too Fast’,” and “Tips for the C-Suite.” The introduction explains containers and microservices in executive language, then warns against ignoring container risk or adding “yet another security point product.” The middle sections argue that containers should be secured inside an overarching cloud security strategy and introduce “The Container Security Triad” as “build, deploy, and run.” The final section, “Tips for the C-Suite,” gives executives questions to ask their CISO, CIO, or CTO about whether containers are integrated into cloud security strategy.
Why it works
- Our readThe opening joke about a “hole in your Docker” makes a technical risk legible to executives before the piece defines the terms.
- Our readThe article separates the upside of containers from the security problem, so the argument does not sound like resistance to speed.
- Our readEnding with questions for the C-suite turns the point of view into a conversation an executive can have with technical leaders.
What not to copy
Don't copy the Docker pun, container topic, or Palo Alto Networks' triad language. Keep the structure of defining a technical shift, naming the executive risk, and ending with questions leaders can ask internally.
More from Palo Alto Networks


More executive briefs
Steal it for your brand.
Tell us what you want to make. We’ll talk through how to put these ideas to work for your brand.