free supply chain threat response guide
Security teams dealing with open-source supply chain attacks see LinkedIn image ads for a free guide, land on Semgrep's 'Automating Open-Source Malware Defense with Semgrep' page, and are asked to submit a form.
Traced from live ads, Nov 17, 2026 · All Semgrep's ads in this campaign →
Security teams responsible for open-source supply chain threat response
Registry attacks create the question 'did this hit us?' and require seeing everything, everywhere, immediately
A guide or playbook on assessing exposure, finding affected repos, analyzing impact, and blocking malicious packages
None on the page
Submit email, first name, last name, and company / organization
The journey
Swipe or scroll sideways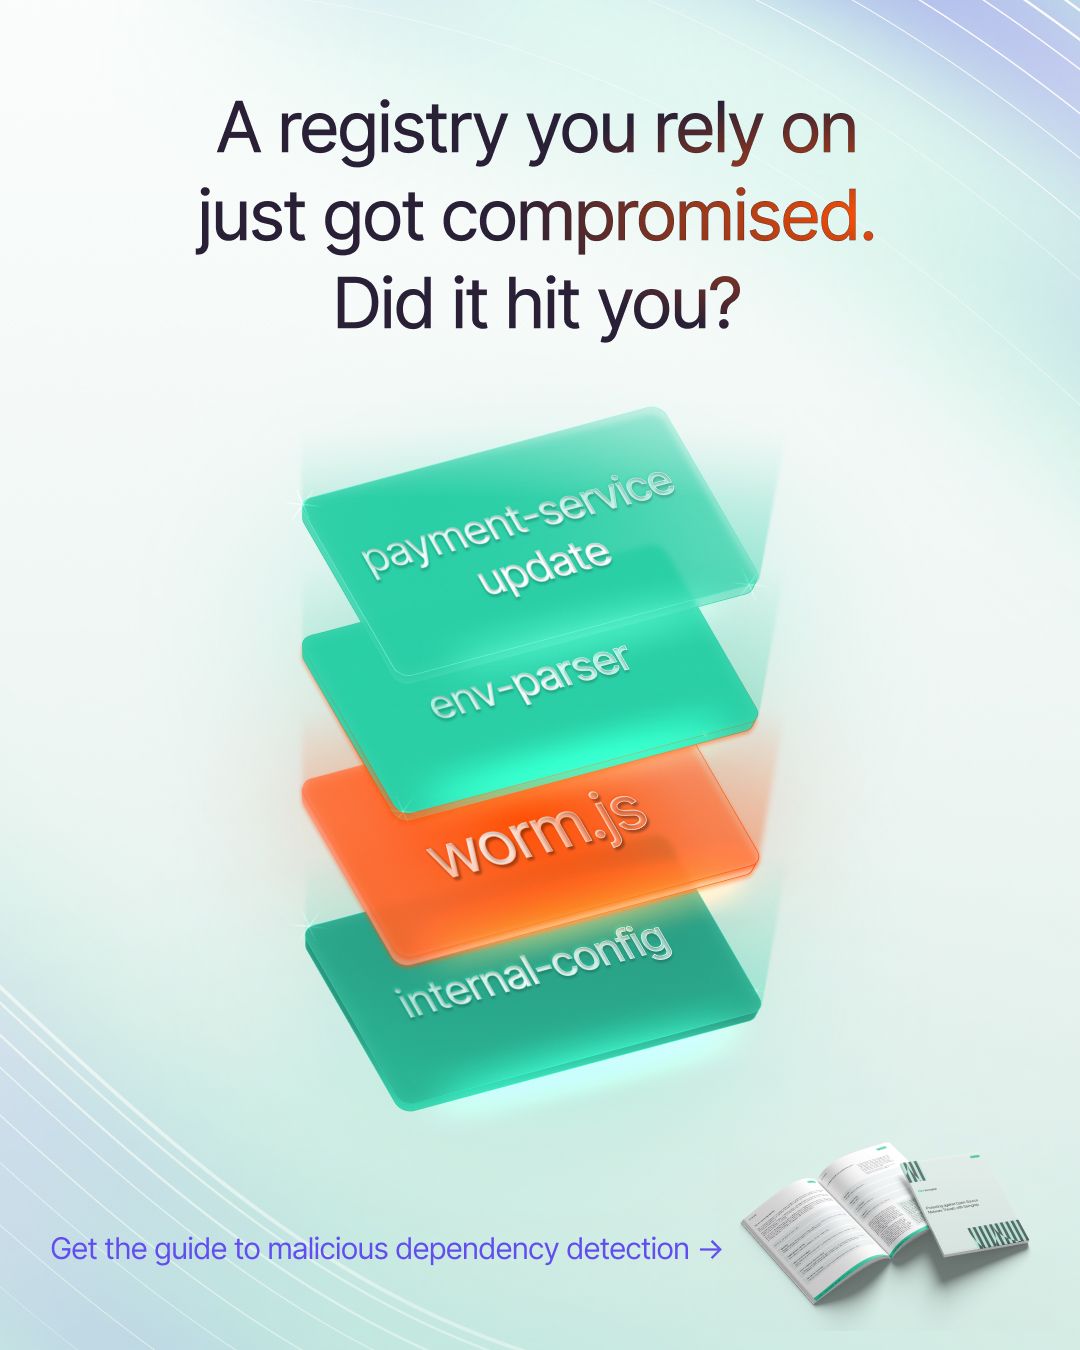
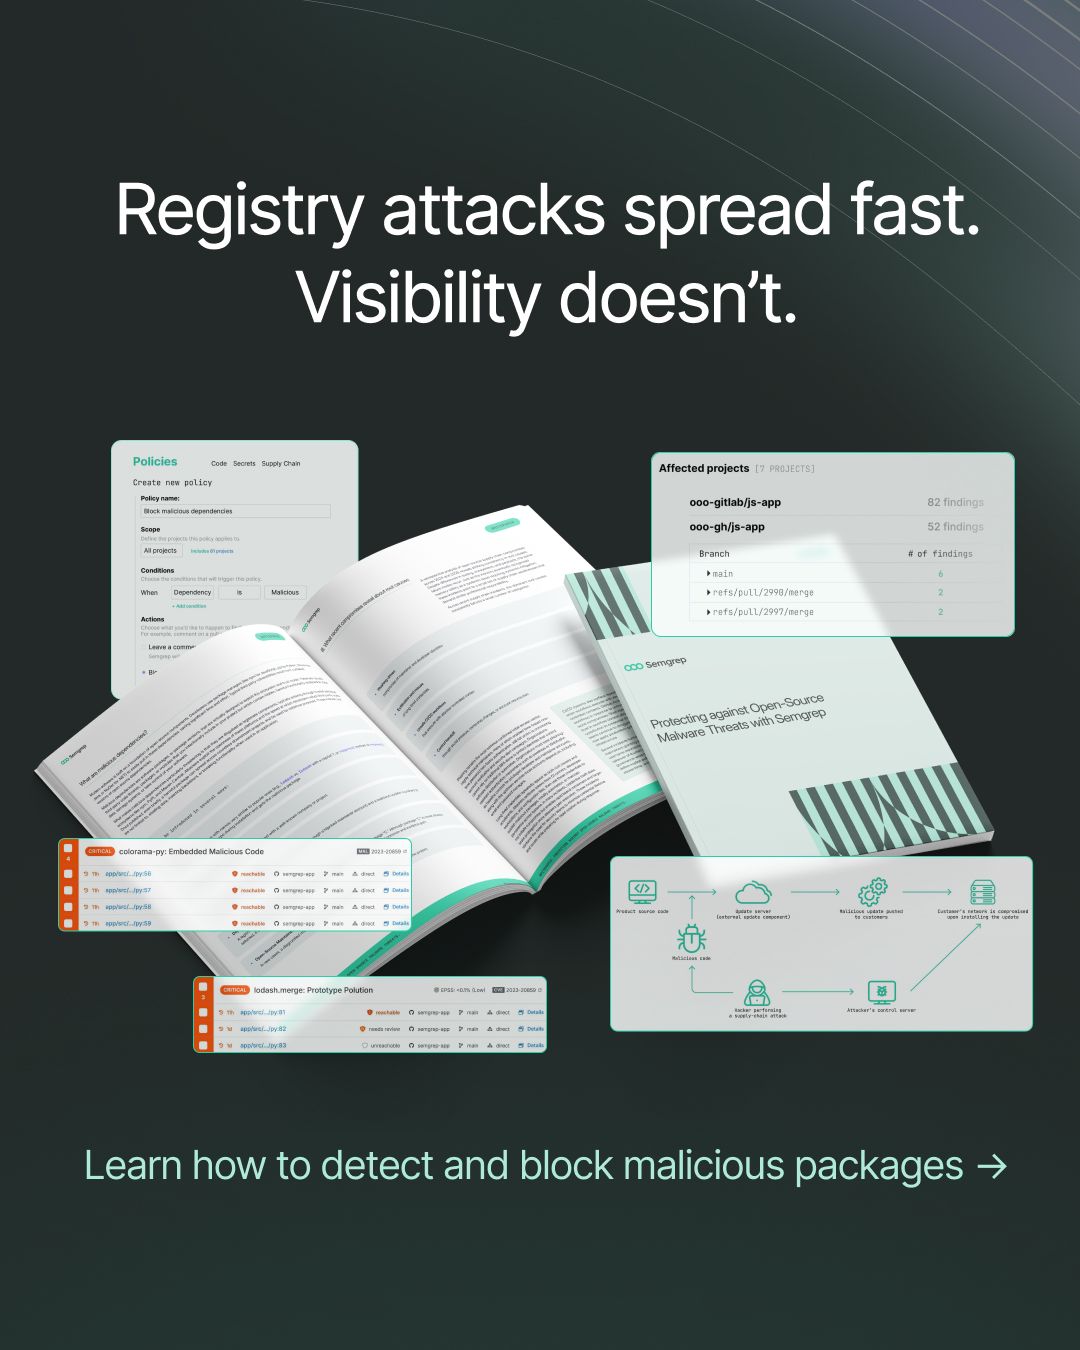
LinkedIn image ads use the headline 'Get our free supply chain threat response guide' and link to Semgrep's resource page on automating open-source malware defense.
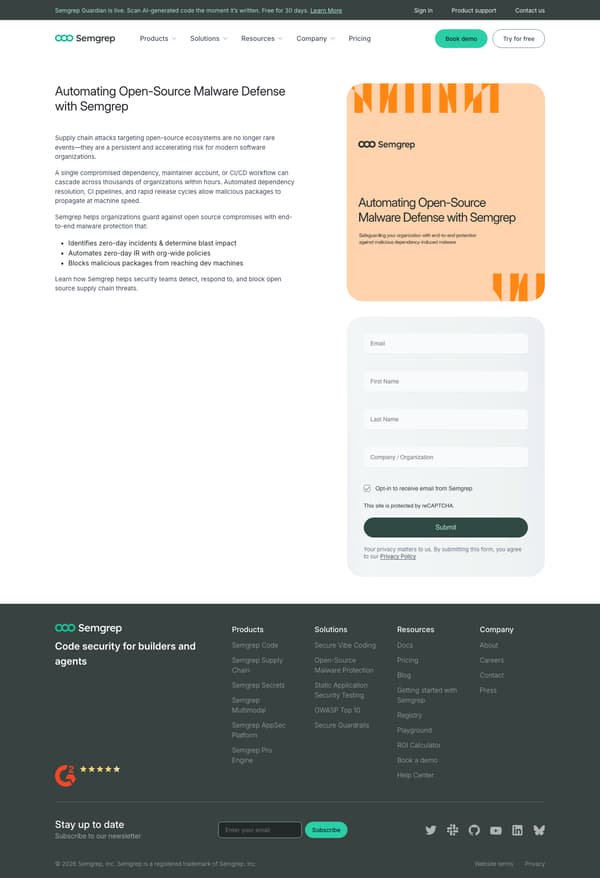
The page leads with 'Automating Open-Source Malware Defense with Semgrep' and says Semgrep helps detect, respond to, and block open source supply chain threats before asking for a form submission.
Steal this campaign.
Tell us what you want to make. We’ll talk through how to put these ideas to work for your brand.
More campaigns